

AEGIS
AI powered cybersecurity command center that thinks at adversary speed.
Attackers automate. Defence has to as well. The Imperium AI Cybersecurity Command Center fuses detection, hunting, deception and response into one agentic loop — investigating every signal, building the attack narrative, and containing threats while your analysts stay firmly in command.
AI CHANGED THE THREAT. IMPERIUM CHANGED THE DEFENCE.
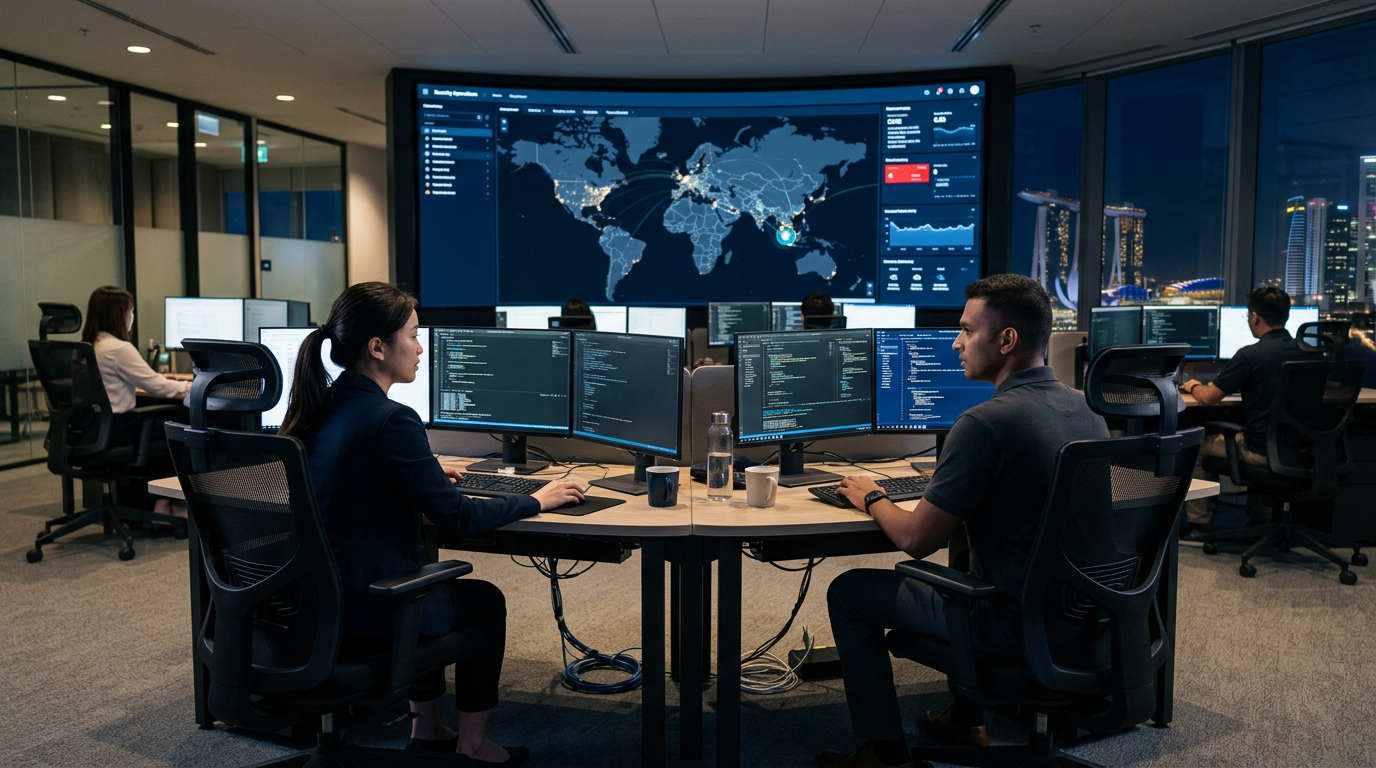
The problem was never detection. It was everything after it.
Most security teams already generate more signal than they can process. AI changes the constraint from analyst hours to decision quality.
Nothing goes uninvestigated
Agents triage and enrich 100% of alerts with asset, identity, exposure and threat-intel context — including the ones humans would have closed unread.
Adversary narrative, not alert lists
Related signals are assembled into a single timeline showing initial access, movement, objective and blast radius.
Containment in the same breath
Isolate hosts, revoke sessions, disable identities and block infrastructure through governed SOAR playbooks with approval gates.
In the age of Mythos and AI driven attacks , five capabilities that dramatically shorten the adversary’s windows
Deploy alongside your existing SIEM, XDR and SOAR investments — the command center orchestrates them rather than replacing them.
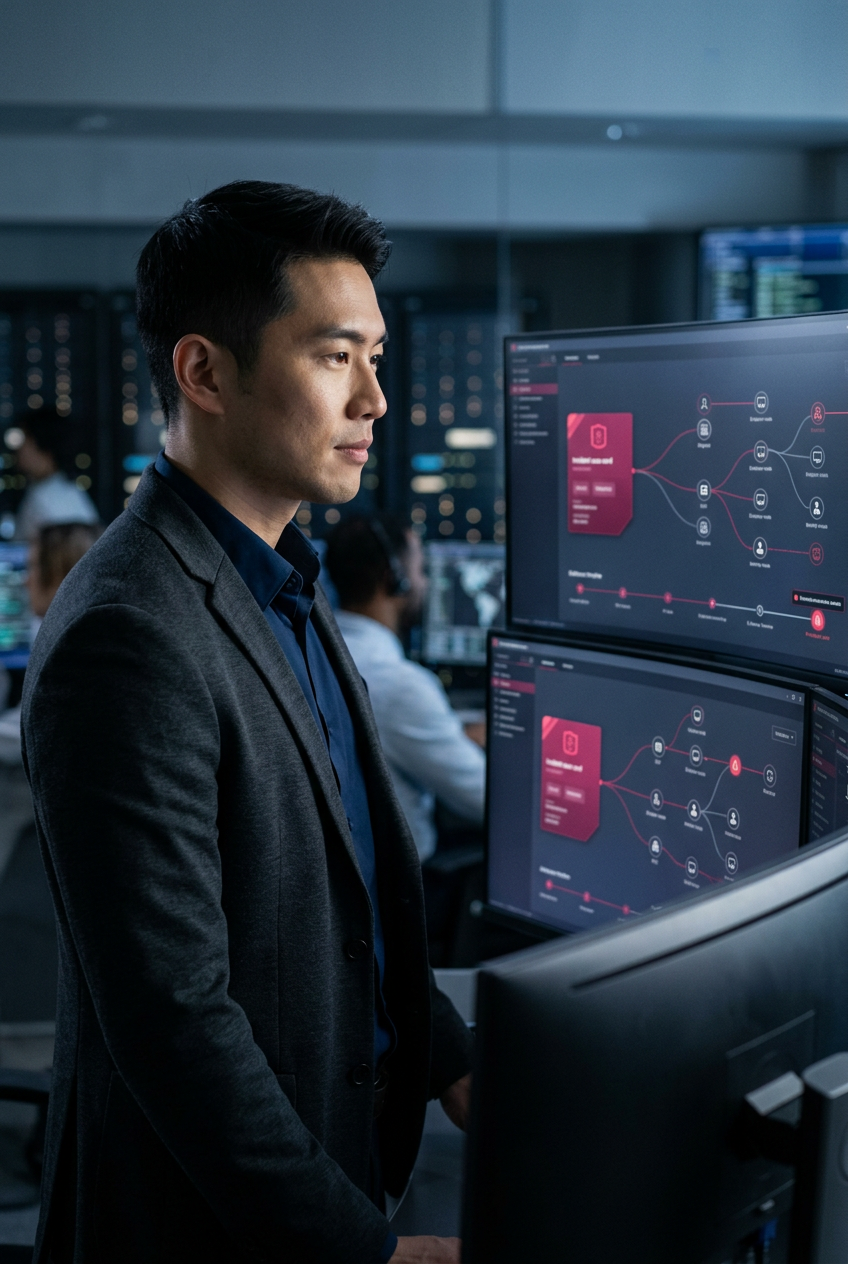
Agentic triage, investigation and response
Every alert gets a full investigation. Agents gather context, test hypotheses, correlate across the kill chain and produce an analyst-grade case file — with a recommended, executable response.
- Automated enrichmentAsset criticality, identity risk, exposure, intel and historical behaviour attached instantly.
- Hypothesis testingAgents pull the additional evidence a senior analyst would have asked for.
- Case narrative generationA readable timeline and impact statement, ready for handover or escalation.
- Governed containmentResponse playbooks with role-based approval gates and complete action logging.

Threat hunting, deception and adversary intelligence
Waiting for a detection to fire cedes the initiative. Continuous hunting and active deception surface adversaries that signature-based controls miss.
- Continuous hypothesis huntingAgents run hunt packs mapped to MITRE ATT&CK across your telemetry.
- Deception gridsDecoy hosts, credentials and documents that generate high-fidelity intrusion signals.
- Adversary emulationScheduled purple-team exercises that validate detection and response coverage.
- Intelligence fusionSector, regional and dark-web intelligence contextualised to your actual exposure.
Identity, insider risk and AI-era exposure
Identity is the modern perimeter — and generative AI has widened it. The command center governs both human and machine identities, including the AI agents your business is now deploying.
- Identity threat detectionSession anomalies, token theft, MFA fatigue and privilege escalation surfaced in real time.
- Insider and data riskBehavioural analytics across exfiltration paths, without blanket surveillance.
- AI and LLM securityPrompt injection, model abuse, data leakage and shadow-AI discovery.
- Non-human identity controlService accounts, agent credentials and API keys inventoried and governed.

Compliance, assurance and executive reporting
Regulators and boards want evidence, not assurances. Control effectiveness is measured continuously and rendered into the language each audience uses.
- Continuous control monitoringLive evidence against MAS TRM, PDPA, ISO 27001 and internal policy.
- Coverage analyticsDetection coverage mapped to ATT&CK, with gaps prioritised by relevance.
- Board-level risk narrativeQuantified cyber risk posture reported in business terms.
- Incident retrospectivesAutomatically drafted post-incident reviews with tracked remediation actions.

Continuous vulnerability and exposure remediation
Finding weaknesses only matters when they get fixed. Exposure is driven to verified closure — prioritised, remediated, re-tested and reported against agreed timelines.
- Exposure-driven prioritisationVulnerabilities ranked by exploitability, reachability and business impact — not CVSS score alone.
- Automated fix orchestrationPatch, configuration and code-change workflows run by agents under change-approval gates.
- Verified closureRemediation confirmed by re-testing and telemetry, not by closing the ticket.
- SLA-tracked debt reductionOpen exposure tracked against agreed timelines with executive visibility.
Where it pays off first.
Command center capability without building one from scratch.
Imperium brings two decades of cyber delivery in Singapore and across Asia — architecture, engineering, and a managed defence service that runs alongside your team.
Assess and architect
Threat modelling, detection coverage assessment, SOC maturity review and a costed command centre blueprint.
Engineer and integrate
Detection engineering, SOAR playbooks, deception deployment and AI guardrail implementation.
Managed detection & response
24×7 monitoring, hunting and response by Imperium analysts working the same agentic platform.
How we get you there.
Establish visibility
Consolidate telemetry, validate log coverage and close the blind spots that make investigation impossible.
Automate triage
Deploy enrichment and triage agents against live alert volume. Measure investigation quality and time saved.
Activate response
Introduce governed containment playbooks, deception grids and continuous hunting.
Drive remediation
Prioritise findings by exploitability, route fixes to the teams that own them and verify every risk is actually closed.
Assure and report
Turn on continuous control monitoring, executive reporting and transition to managed defence.
Best-of-breed security, assembled and operated by Imperium.
Each layer of the command center runs on a leading platform, integrated and tuned as one feedback loop. Already running one of these — or shortlisting it? Send us an enquiry and we will show you how it fits the unified center.
Splunk
SIEM · analyticsIndex, search and correlate machine data at scale — the telemetry backbone of the command center.
Elastic
Search · security analyticsOpen search and analytics engine powering SIEM, detection rules and fleet-wide log mining.
Vicarius
Endpoint remediationAI-powered vulnerability discovery, prioritization, patching, and patchless protection.
Vectra AI
NDR · AI detectionAI-driven network detection and response; finds attackers by behaviour, not signatures.
Exaforce
AI SOCAgentic SOC platform built on a real-time security knowledge graph.
Illumio
Containment · microsegmentationAdaptive segmentation that limits lateral movement and blast radius.
Mimecast
Email securityEmail and collaboration security; stops phishing, spoofing and data loss at the gateway.
Tenable
Exposure managementContinuous vulnerability and exposure discovery across cloud and on-premises assets.
Nexthink
Endpoint visibilityReal-time endpoint telemetry; see what users actually experience and remediate instantly.
Tanium
Endpoint managementReal-time visibility and control across every device, at fleet scale.
Zest
Cloud securityAI-driven cloud risk resolution; finds and fixes misconfigurations and identity risks automatically.
CleanStart
Software supply chainProduct-led supply chain security that shifts protection left into the build.
Netskope
SSE · SASESecure access and data protection across web, cloud and private applications.
Aqua Security
Cloud-native securityContainer, serverless and cloud workload protection across the full lifecycle.
SentinelOne
AI SOC · AI SIEM · XDRTelemetry analytics, detection, investigation, hunting, response intelligence.
Trend Micro
XDR · platformBroad AI-powered XDR coverage across endpoint, cloud and network.
Proofpoint
Human-centric securityProtects people and data from targeted email, phishing and insider threats.
CrowdStrike
AI XDRThe Falcon platform: AI-native endpoint protection, threat hunting and incident response.
Horizon3
Adversary validationAttack-path discovery and proof-by-exploit; verifies closure after every fix.
Fastly
Edge cloud · WAFEdge delivery, web application firewall and bot defence at global scale.
The rest of the unified center.

AI Future of Work
Your next hire may not be human. Humanoids, quadrupeds and drones, digital humans, agentic AI and a private LLM platform — four modalities that give physical, conversational, procedural and knowledge work a machine counterpart.

AI Network Operations Center
An autonomous network operations center where AI agents observe every device, circuit and workload, predict degradation before users feel it, and remediate without waiting for a human ticket.

AI Digital End User Experience
Continuous experience telemetry, self-healing endpoints and a digital twin of the workplace — measuring how work actually feels for every person, then fixing it before anyone complains.

How long would an intruder last?
We will run a coverage and containment assessment against your current stack and show you exactly where the adversary's window is still open.